Flagship · Documented lab
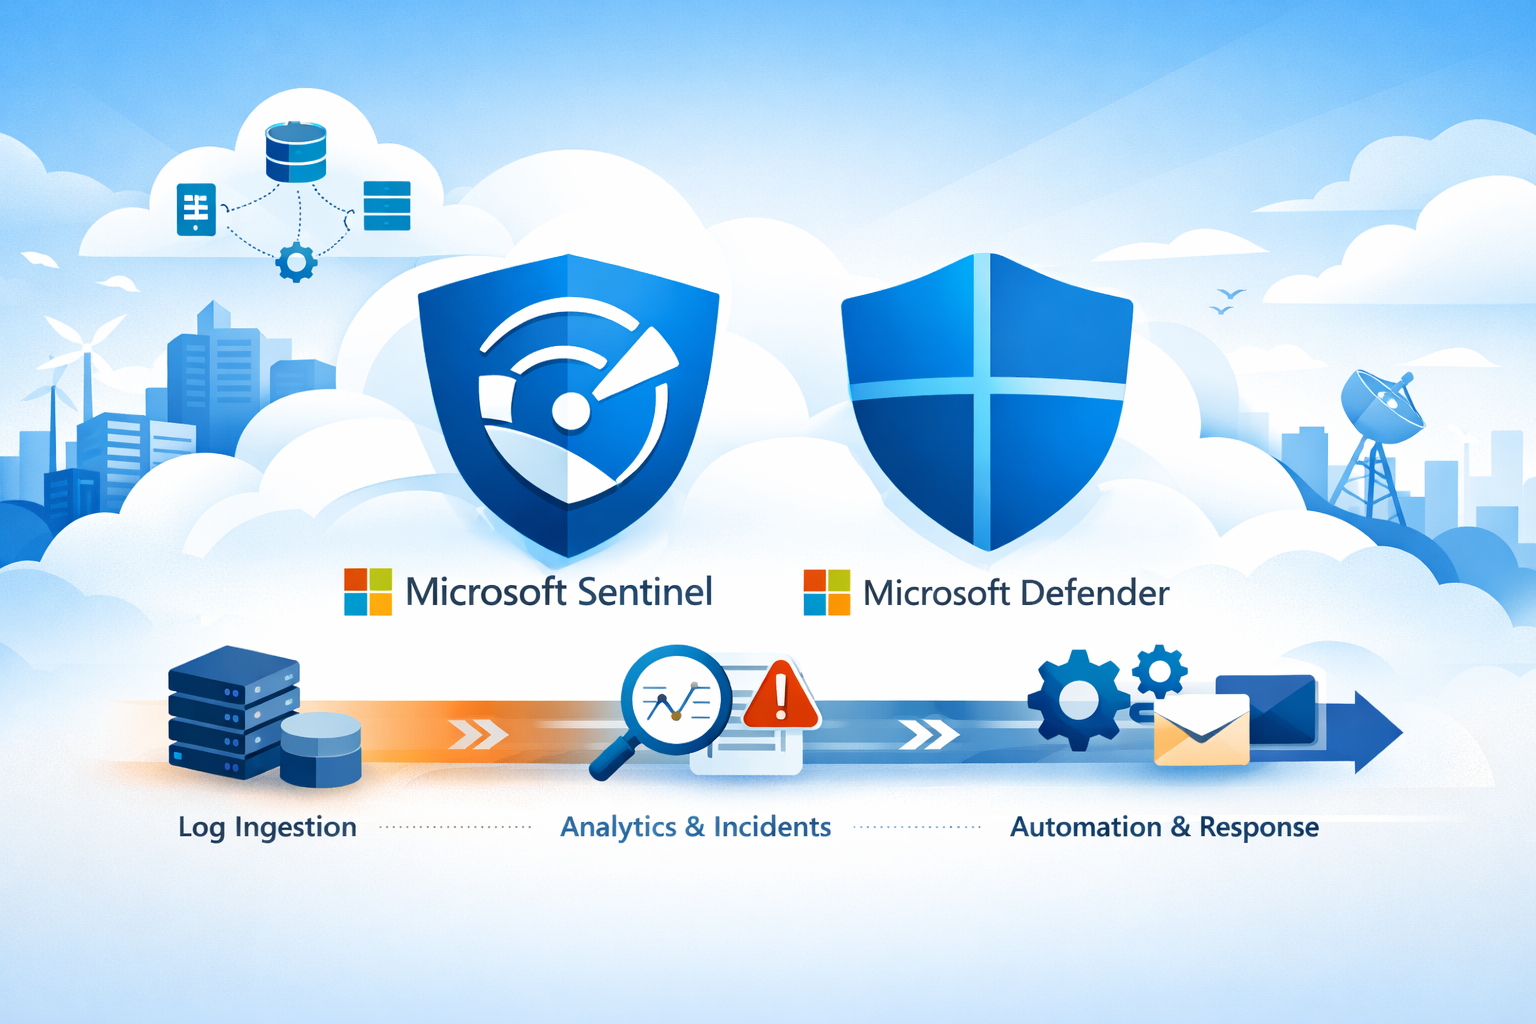
Microsoft Sentinel + Defender Lab (Azure SIEM/SOAR)
Cloud SIEM/SOAR lab demonstrating Azure log ingestion, KQL detections, incident generation, and tested Logic Apps automation.
Portfolio index
Labs, analyst tools, and case studies. Featured work leads; all existing project routes remain available.
Flagship · Documented lab
Cloud SIEM/SOAR lab demonstrating Azure log ingestion, KQL detections, incident generation, and tested Logic Apps automation.
Project
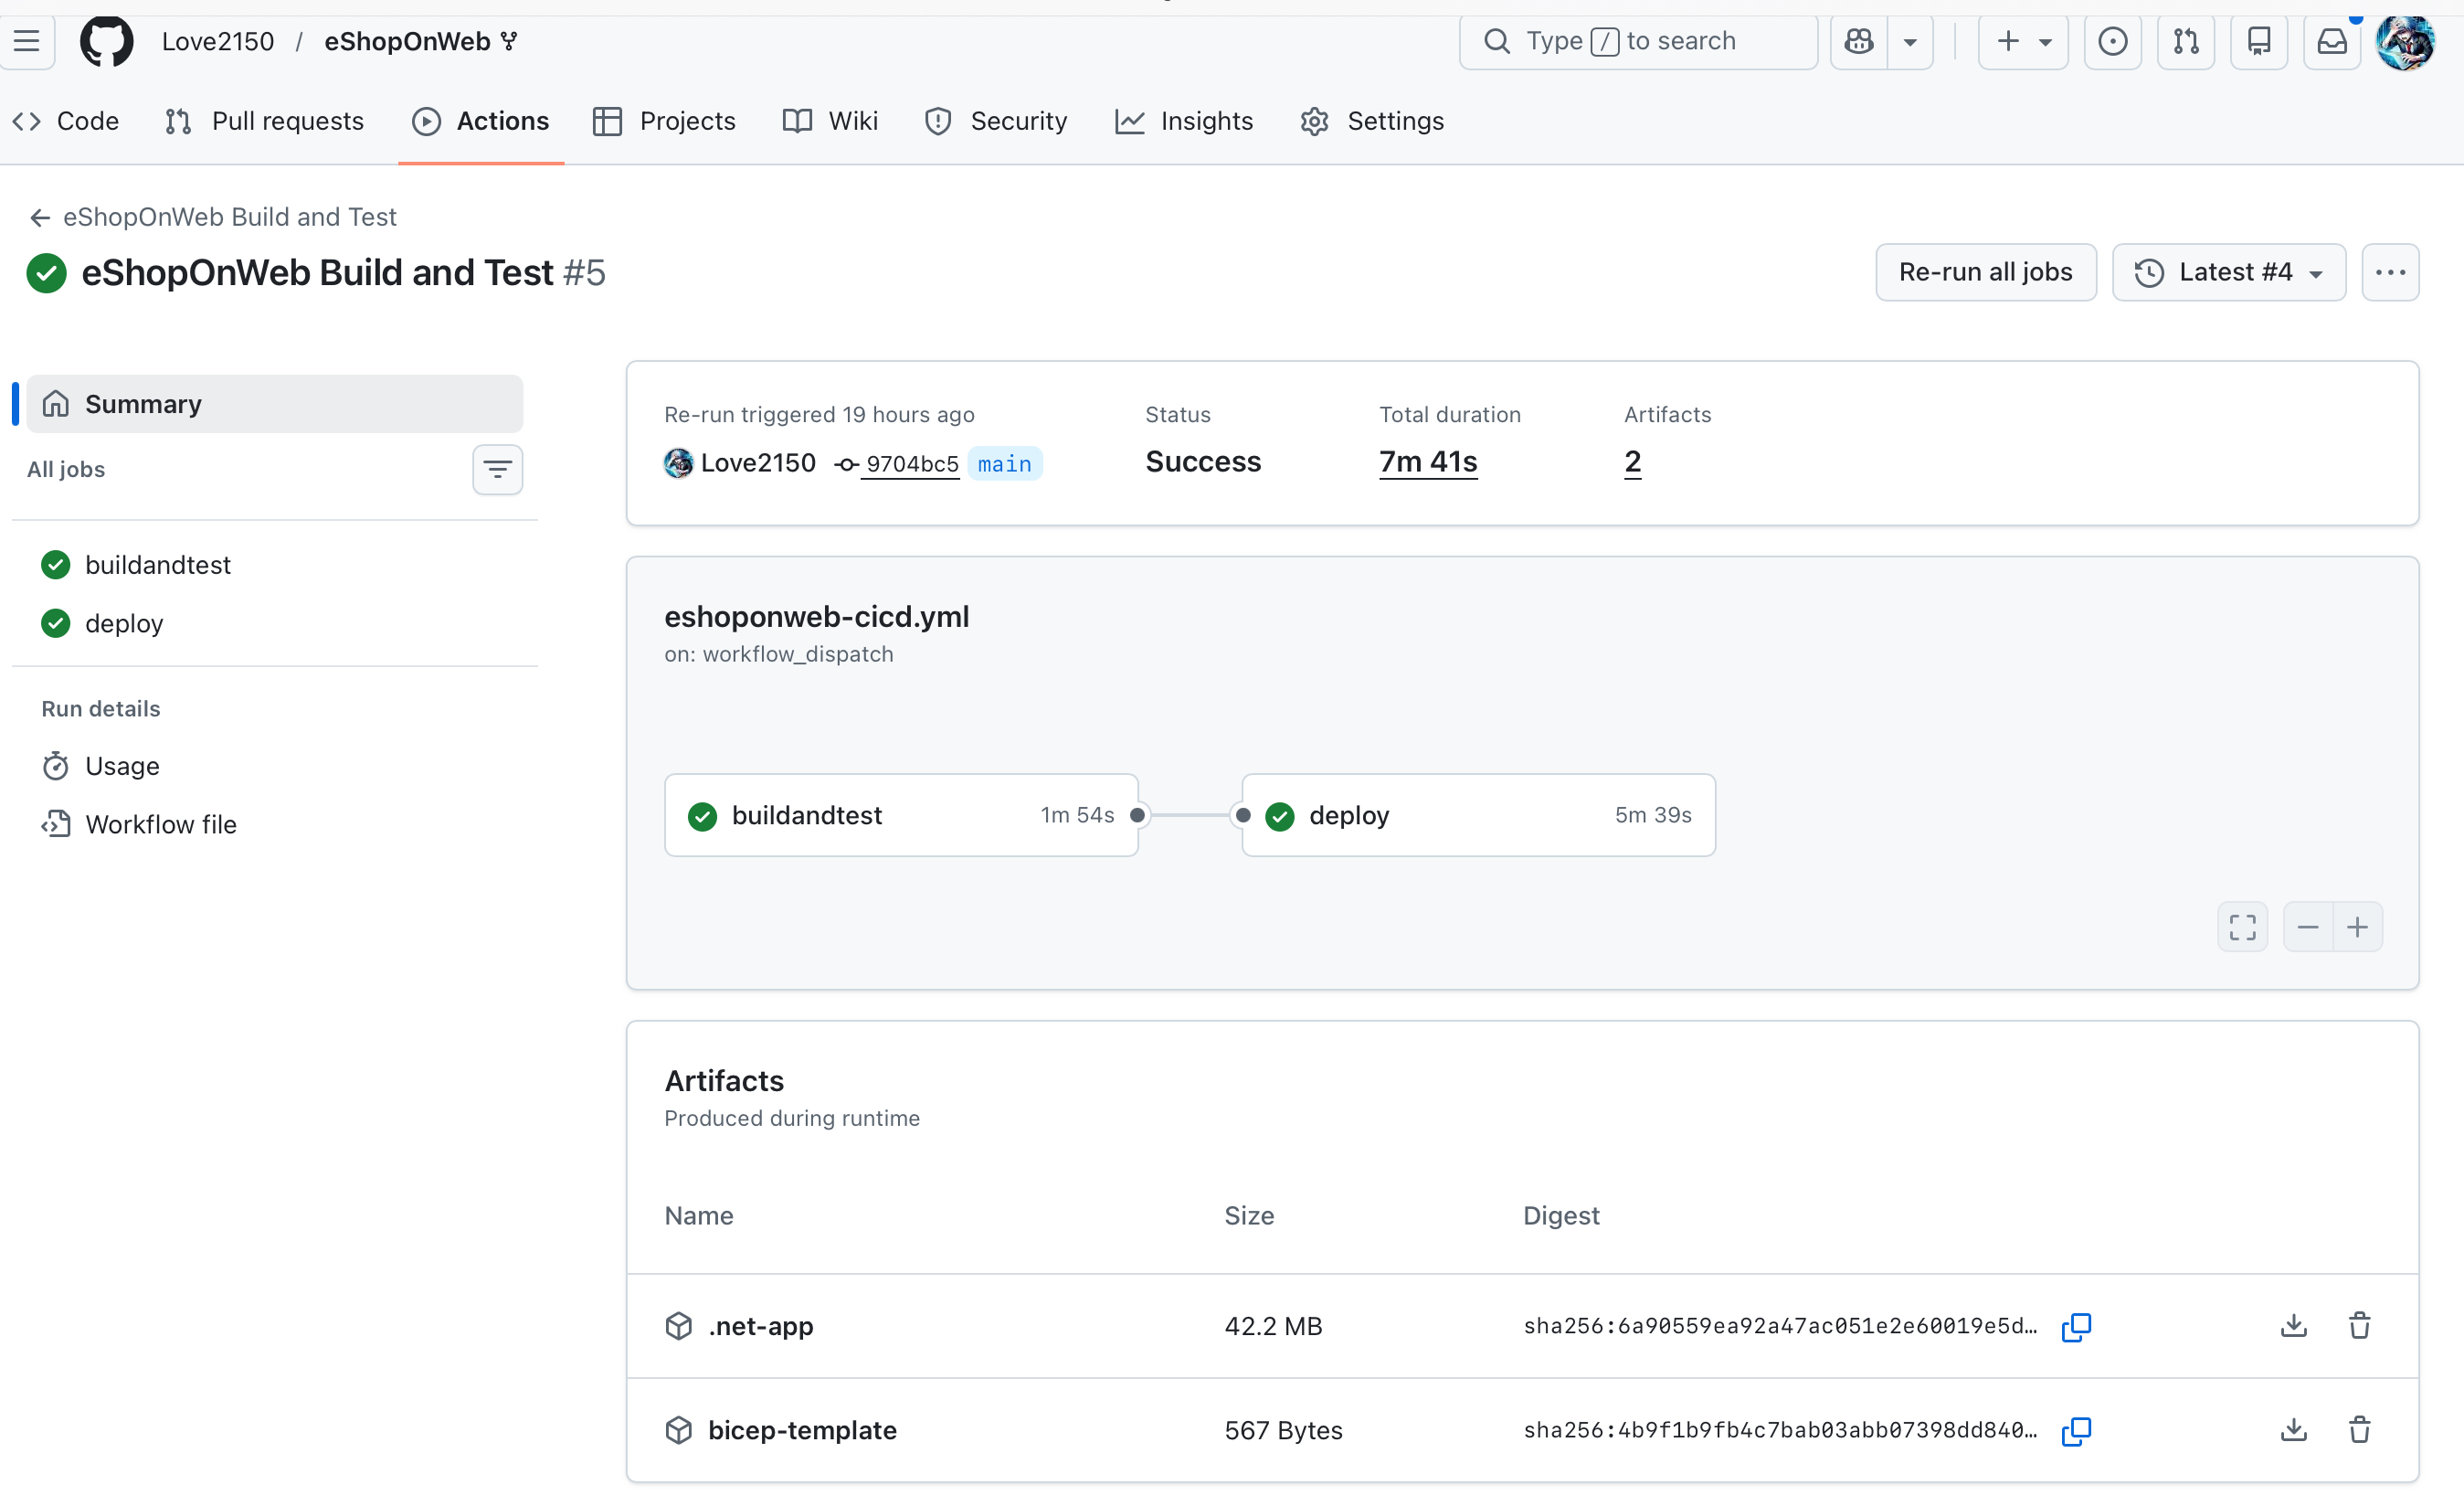
Secure planning, PR-based change control, CI/CD + IaC, and resiliency testing with Azure + GitHub.

Project
Responsive portfolio with a Jekyll-powered blog, Medium-to-Markdown autosync, and custom blog/projects sliders.
Eight phases passed separate fail-closed review
A phased security-engineering program covering hostile-input handling, analytical correctness, Python packaging, evidence provenance, CI/CD, and release governance.

Tested portfolio tool
Bounded reconstruction of classic eval(function(...)) JavaScript packer payloads without executing recovered code.

Flagship · Tested portfolio tool
Installable EVTX/Sysmon triage with parser-completeness metadata, validated IOCs, lightweight rules, and protected reports.

Flagship · Tested portfolio tool
Installable PCAP triage with complete-capture statistics, HTTP/TLS evidence, CSP-protected reports, and public-unicast-filtered VirusTotal enrichment.