Case 01 · SIEM / SOAR
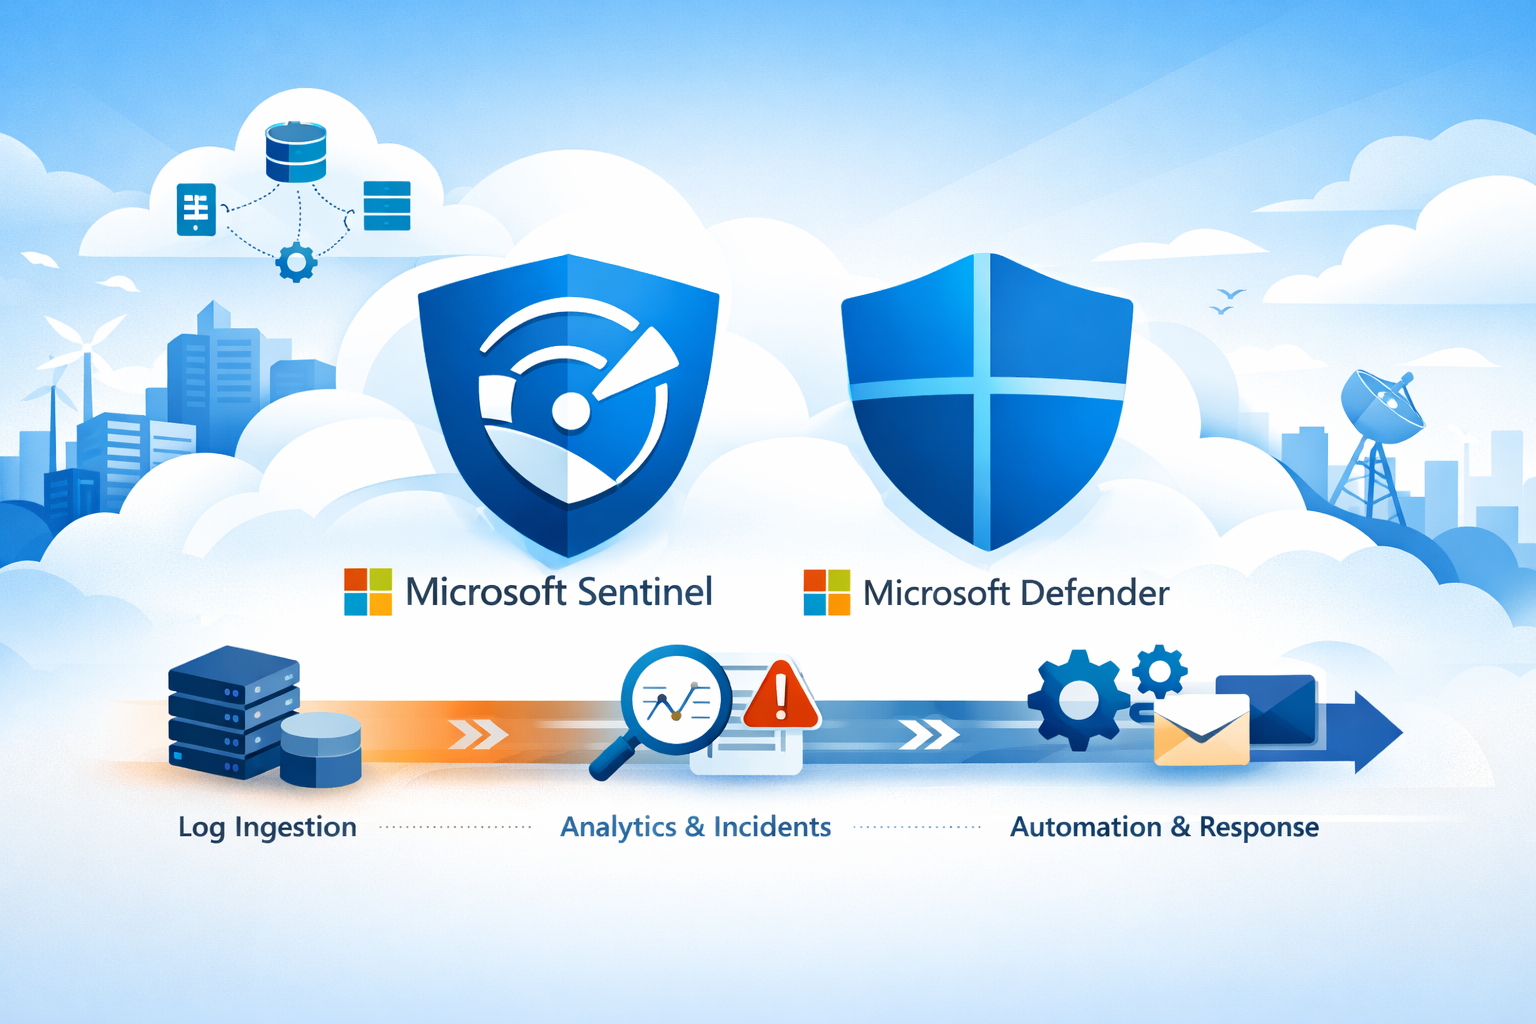
Microsoft Sentinel + Defender
- Problem
- Prove an end-to-end cloud security operations path from telemetry to response.
- Built
- Log Analytics ingestion, KQL analytics, Sentinel incidents, and a Logic Apps enrichment playbook.
- Validation
- Made a controlled NSG rule change and checked the event, rule, incident, and playbook path.
- Outcome
- The case file documents Azure Activity ingestion, KQL analytics, incident triage, and successful Logic App run history.

